The event has already taken place, thanks for checking!

Sign up for the event before time runs out and receive a free t-shirt
The event has already taken place, thanks for checking!

Join Proofpoint and Deloitte for an exclusive session on how Canadian healthcare organizations can stop data loss before it happens with human-centric, adaptive DLP. Discover how to prevent misdirected emails, protect sensitive health information, and stay ahead of insider threats in today’s digital-first world.
By joining this webinar, you’ll gain:
Don’t leave patient data and your organization’s reputation vulnerable. Learn how Proofpoint can help you protect what matters most.
Become the ultimate cybersecurity hero and embark on a quest like no other, where every click and keystroke brings you closer to mastering the art of cyber defense. Join your fellow cybersecurity peers for Proofpoint Defenders, an interactive journey into human-centric security. Harness the strength of Proofpoint’s People Protection platform to compete live with other players to stop threats from treacherous phishing schemes to relentless malware assaults leveraging multi-layered, AI-augmented email threat defense and a chance to win amazing prizes! With our cutting-edge tools at your fingertips, you'll uncover hidden dangers, outmaneuver cyber villains, and shed light on the human element of security to emerge as the true champion of digital justice. At this Capture the Flag event, you’ll get to:
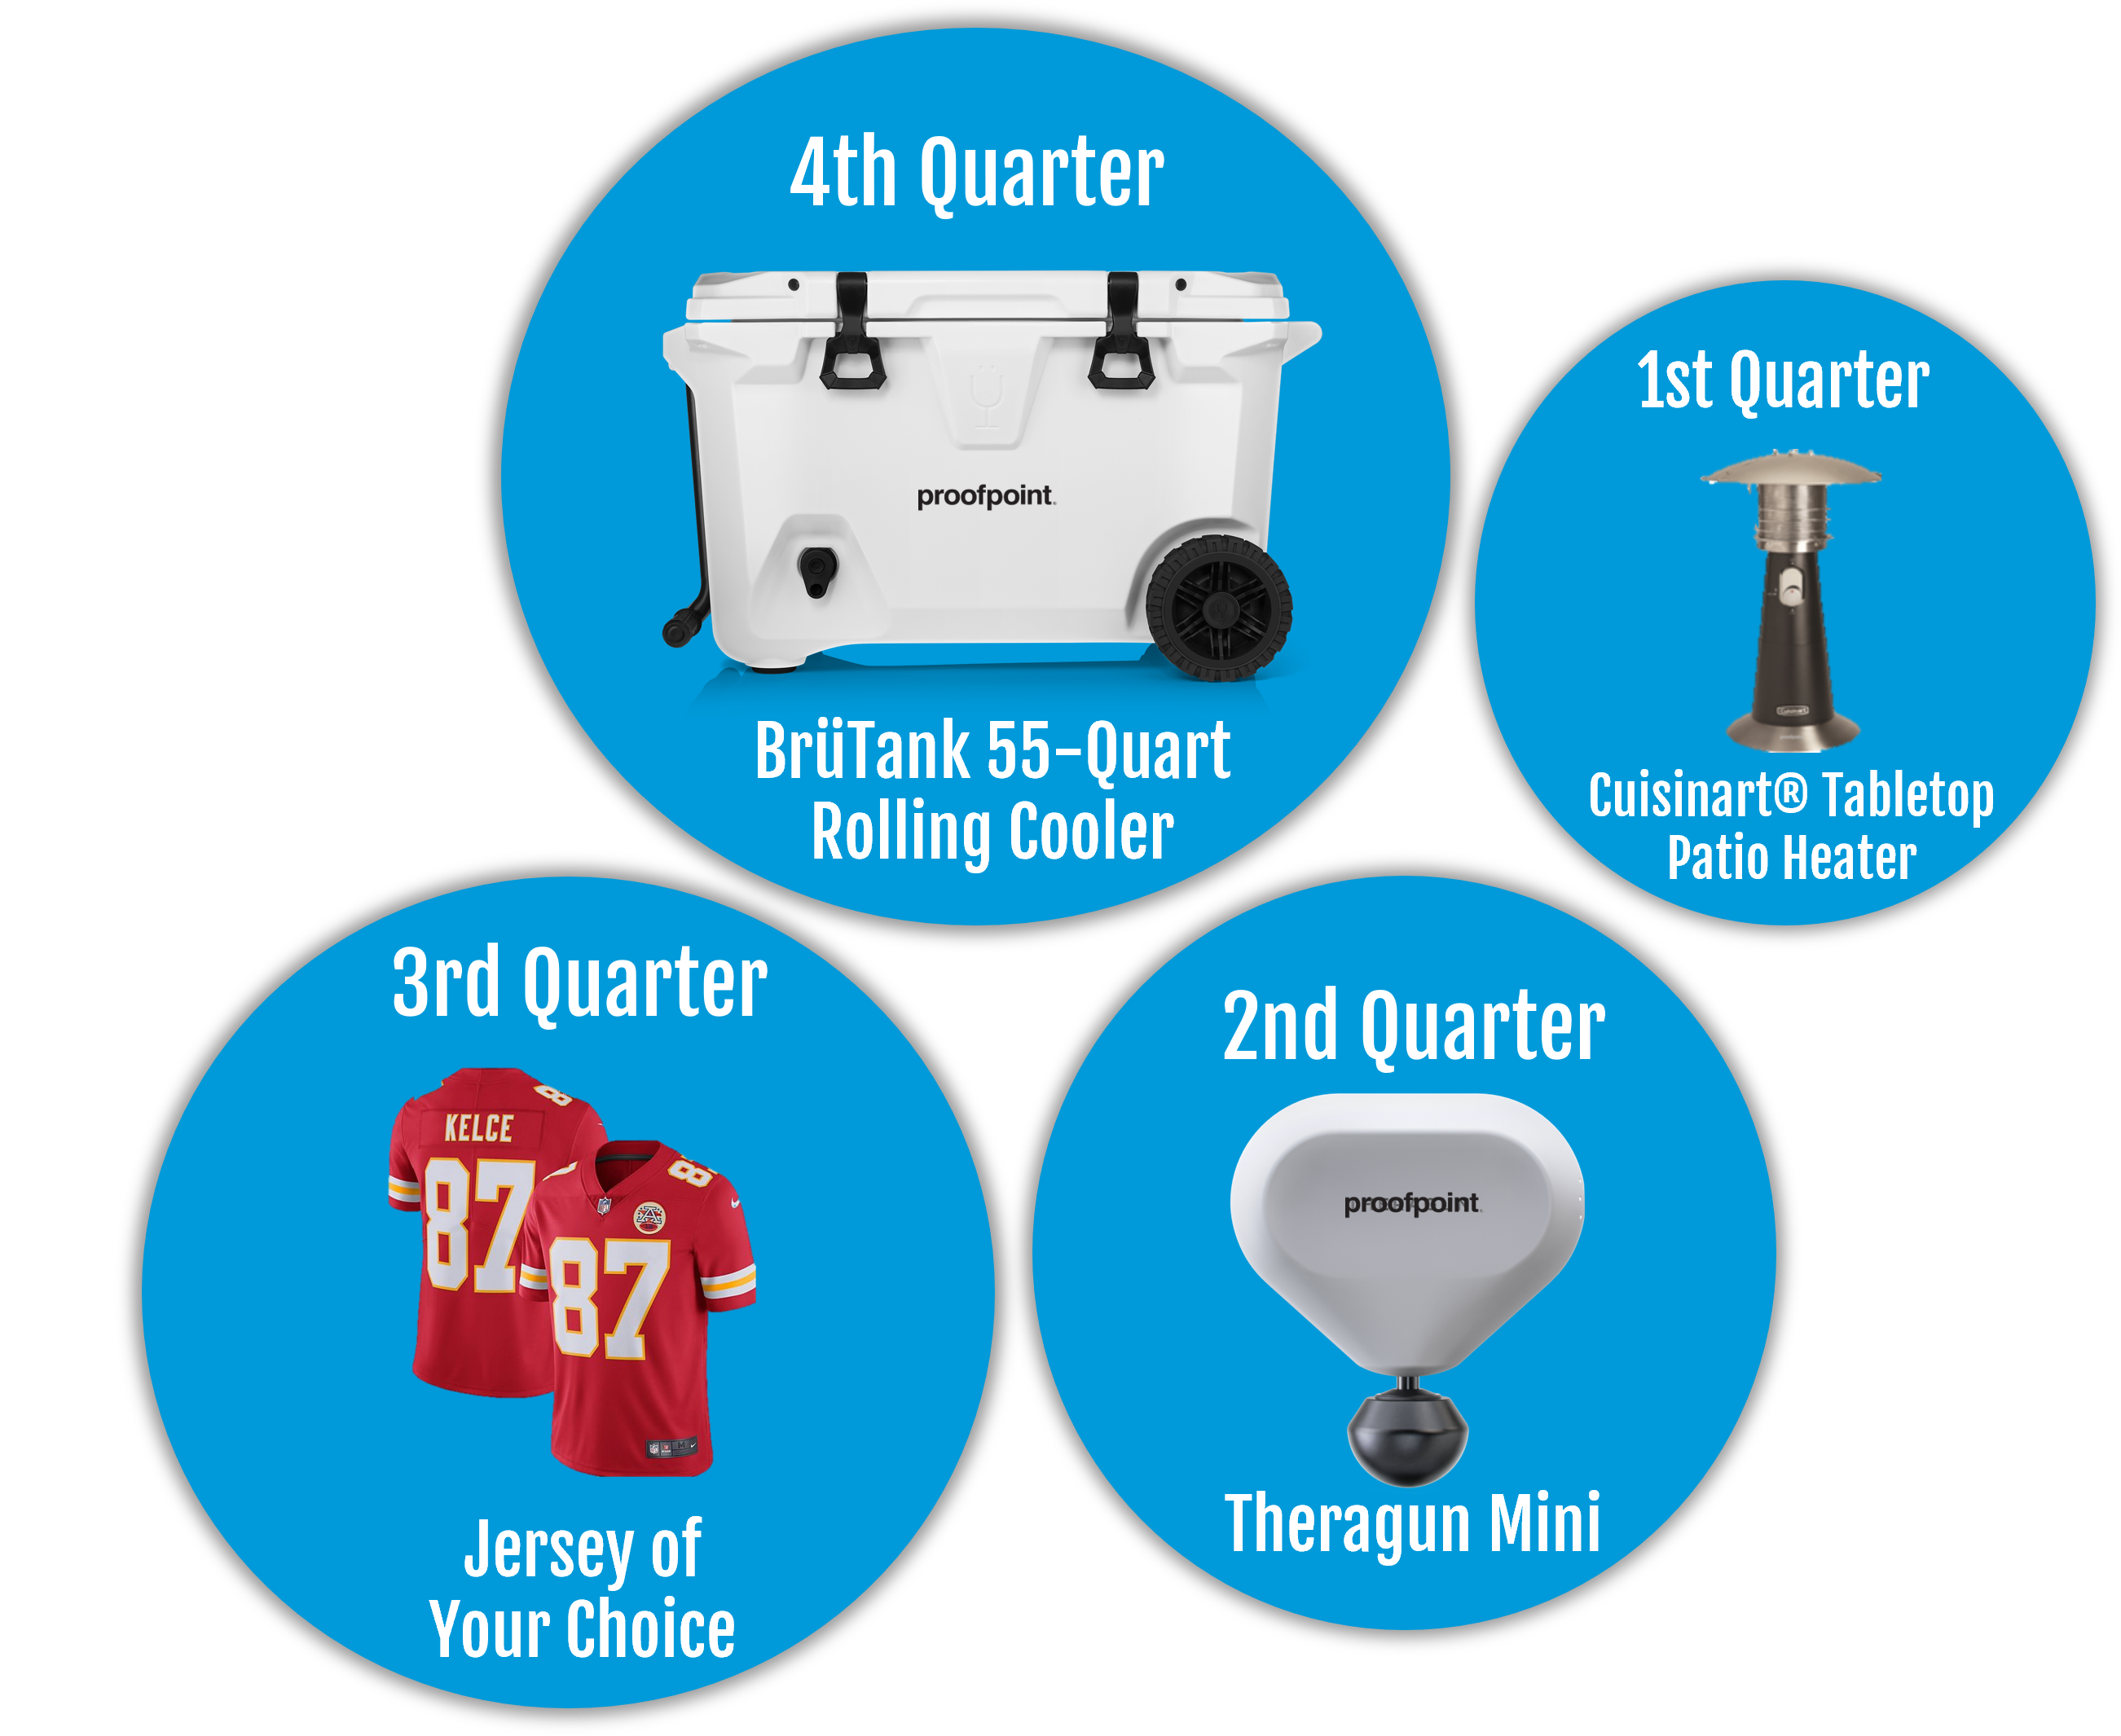
Prizes will be awarded to the Top 3 Defenders (winners have the option to decline prizes). They are determined by highest scores, time to complete, or both.
You'll receive this badge upon completion of Proofpoint Defenders, designed to help organizations stop email threats including business email compromise, ransomware, and credential phishing.
You'll receive this badge upon completion of Proofpoint
You'll receive this badge upon completion of Proofpoint
You'll receive this badge upon completion of Proofpoint
You'll receive this badge upon completion of Proofpoint
Curabitur erat felis, porttitor ac iaculis sed, egestas eu nulla. Aliquam placerat ultricies eros, facilisis hendreit turpis. Optional text section. Can be toggled on/off.
CISOonline South
Virtual | 11:00
am-11:45 am ET
Identity Deception Healthcare
SHERATON
CENTRE | 123 Queen St W Toronto M5H 2M9 Canada
Proofpoint Usergroup Federal
Virtual,
USA
CISOonline South
Virtual | 11:00
am-11:45 am ET
Identity Deception Healthcare
SHERATON
CENTRE | 123 Queen St W Toronto M5H 2M9 Canada
Proofpoint Usergroup Federal
Virtual,
USA
Nulla eleifend dapibus mi, sed tempus sapien placerat quis. Maecenas at orci est. Nulla mattis, juto sit amet alementum tincidunt, metus ipsum pretium nunc, ut eestas dian risus efficitur nulla. Dus assumsan, ligula non malesuada consequat, sem nunc pulvinar.
Optional text section. Can be toggled on/off.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
Optional text section. Can be toggled on/off.
Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum. Cras non pharetra massa. Sed quis sodales neque. Fusce consequat eget nibh ut condimentum. Vivamus tempor vitae sapien eget scelerisque.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
In libero ex, luctus vel consectetur sit amet, lacinia sed nisi. Phasellus at vulputate augue. Aenean id semper elit, facilisis rutrum libero. Curabitur blandit pretium accumsan. Proin scelerisque purus quam, facilisis tristique lectus elementum interdum.
Optional text section. Can be toggled on/off.
Director of Development proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
Chief Technical Officer, proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
EVP, Cybersecurity Strategy, proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
SVP, Systems Engineering and Customer Success, proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
Chief Technical Officer, proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
Director of Development proofpoint
Vivamus male suada eget eu pos uere in bibendum orci id vest.
This event is suitable for information security decision makers, including: CXO, VP of IT, Director of IT; mid-level information security management (Senior Security Manager, IT Security Manager, IT Manager) and technical information security practitioners (Security Engineer, Messaging Architect, IT Analyst). This event is not open to channel or technology partners.
NOTE: Registration requires a valid email address from your organization’s domain, so Gmail, Hotmail, AOL, Yahoo or any other ISP are not accepted.
This event is approved and endorsed by (ISC)2 and CPE credits will automatically be credited to your member account within 4-6 weeks.
Parking Information
Curabitur erat felis,
porttitor ac iaculis sed, egestas eu nulla. Aliquam placerat
ultrcies eros, facilis hendrerit turpis. Pellentesque laoreet
orci placerat lacus condimentum, eu placerat dolor commodo.
Integer Congue Massa
Curabitur erat felis,
porttitor ac iaculis sed, egestas eu nulla. Aliquam placerat
ultrcies eros, facilis hendrerit turpis. Pellentesque laoreet
orci placerat lacus condimentum, eu placerat dolor commodo.
Curabitur erat felis, porttitor ac iaculis sed, egestas eu nulla. Aliquam placerat ultricies eros, facilisis hendreit turpis. Optional text section. Can be toggled on/off.
CISOonline South
Virtual | 11:00
am-11:45 am ET
Identity Deception Healthcare
SHERATON
CENTRE | 123 Queen St W Toronto M5H 2M9 Canada
Proofpoint Usergroup Federal
Virtual,
USA
CISOonline South
Virtual | 11:00
am-11:45 am ET
Identity Deception Healthcare
SHERATON
CENTRE | 123 Queen St W Toronto M5H 2M9 Canada
Proofpoint Usergroup Federal
Virtual,
USA