
Location/Region/Verticle
The event has already taken place, thanks for checking!

Join Proofpoint for an exclusive Insider Risk Summit Dinner!
Before dinner begins, we’ll showcase how organizations can stay ahead of insider-driven risk—before it escalates into a breach, investigation, or regulatory exposure. During a live demonstration, we’ll showcase how modern Insider Threat Management programs evolve from reactive response to proactive prevention as part of the Proofpoint Data Security platform.
Through real-world scenarios, you’ll discover how teams can:
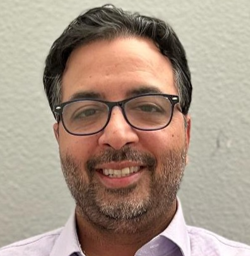
With a background primarily in network, cloud and SaaS Security, Amish has used his technical expertise in sales and administrative roles. Previously, he was a senior sales engineer with Bitglass and Accellion, and a Senior Systems/Security Administrator with Check Point Software Technologies. Amish graduated from San Jose State University.
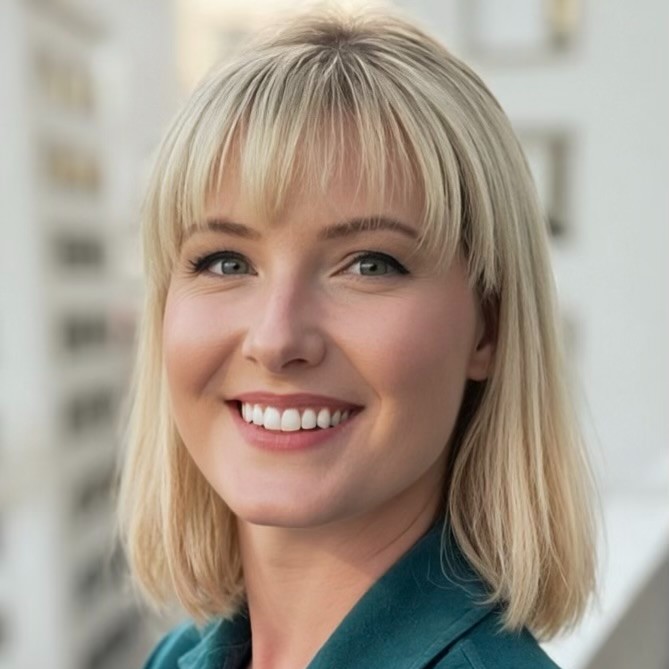
Kasey is a veteran of the United Stated Air Force experienced in Fusion Intelligence, Counterterrorism, and Human Behavioral Analysis. She spent the latter half of her career conducting proactive-focused behavioral and technical analysis for Insider Threat investigations using advanced technologies. She then went on to lead and mature enterprise-wide multidisciplinary Insider Risk Programs for Federal and Fortune 500 Companies within verticals to include Biopharma, Healthcare, and Retail.
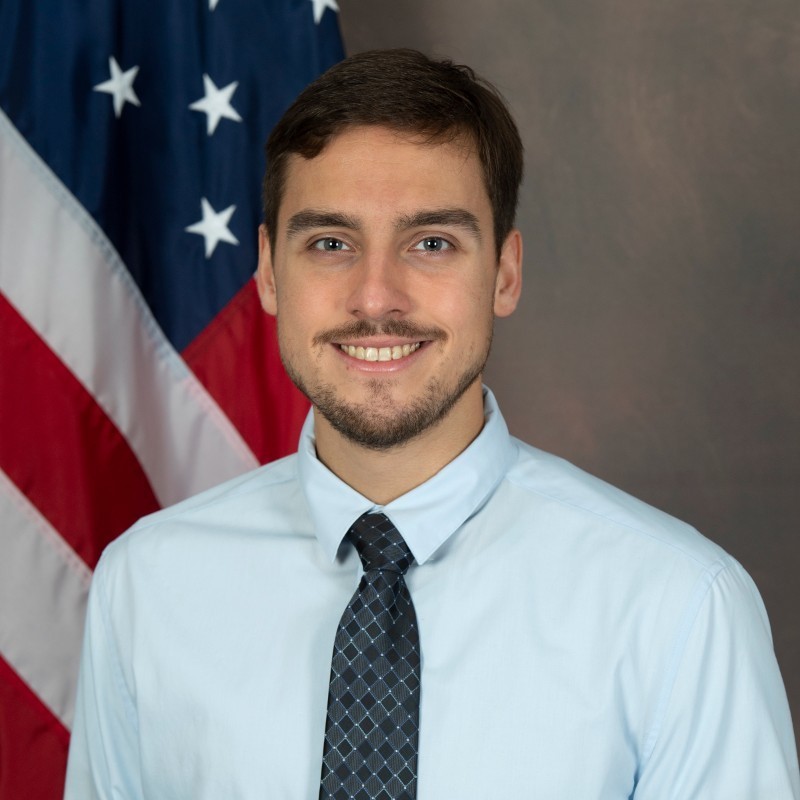
Ryan Bellows is a U.S. Army veteran who served in Operation Inherent Resolve and student at NYU Tandon School of Engineering. Currently, Ryan leads insider risk initiatives at Regeneron Pharmaceuticals. His background spans the Department of Defense and the biopharma industry, with a focus on insider risk, incident response, and detection engineering. Ryan is also a contributor and practitioner in the development and operationalization of the Insider Threat Matrix.
This event is suitable for information security decision makers, including: CXO, VP of IT, Director of IT; mid-level information security management (Senior Security Manager, IT Security Manager, IT Manager) and technical information security practitioners (Security Engineer, Messaging Architect, IT Analyst). It is also suitable for compliance decision-makers, including General Counsel, Chief Compliance or Privacy Officer; mid-level compliance/privacy management (Compliance Manager); and compliance/privacy practitioners (Compliance/Risk Assistant, Compliance Administrator), Insider Risk Program Analysts/Engineers, Insider Risk Managers, Risk Management, Corp Security leaders. This event is not open to channel or technology partners.
NOTE: Registration requires a valid email address from your organization’s domain, so Gmail, Hotmail, AOL, Yahoo or any other ISP are not accepted.